OT Security Expert Training
Three days on real industrial controllers. Read industrial protocols byte by byte, run attacks under control and write the detection rule for them on your own capture.
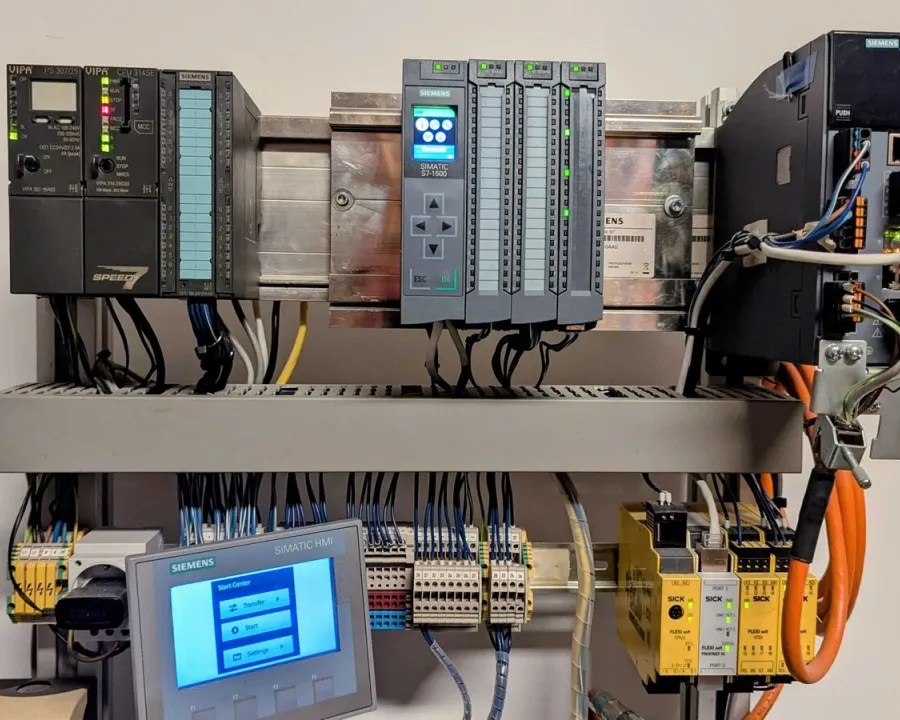
At a glance
The OT Security Expert is our advanced training for hands-on work at the plant. Three days on site, 24 teaching units. Around 80 per cent of the time you work yourself, on real industrial controllers. Day 1 reads the protocols, day 2 runs controlled attacks, day 3 writes the detection on your own captures.
- Duration. Three days, 24 teaching units of 45 minutes.
- Format. On site, in-house or as an open date.
- Language. German.
- Hands-on work. Around 80 per cent.
- Group size. Eight people at most. Two people work at each plant. Larger groups are split across two dates.
- Completion. Final exercise, an incident report of your own and a certificate of attendance.
- Prerequisites. The Professional or comparable practical experience, confident use of Wireshark and the command line, Python at reading level.
We arrange dates on request, for in-house and for open courses alike.
Who this training is for
- People responsible for OT security who have to judge test reports and manufacturer statements on their merits
- SOC and control room staff who run or are introducing detection for industrial protocols
- Automation engineers with security responsibility
- Auditors, consultants and assessors who want to back up findings of their own
Required are the Professional or comparable practical experience, confident use of Wireshark and the command line, and Python at reading level. Scripts are adapted, not written from scratch. For beginners the training is too dense.
Afterwards you can
- Take a capture apart field by field, even where the analysis tool does not decode it
- Open up an address space without a project file
- Work through an unknown protocol in a structured way
- Say before the work what a test action triggers, who approves it and how to undo it
- Phrase a finding at a traceable level of evidence and name what remained unchecked
- Change process values and device identities and judge the consequences for plant and control room
- Write detection rules and YARA signatures and assess rules written by others
- Connect OT sources to a SIEM and formulate use cases for them
- Build a baseline and find deviations without a signature
- Write a technical incident report, including the reporting duties under NIS2
Anyone who wants to build the fundamentals first, from the components of a plant through its protocols to IEC 62443 and NIS2, belongs in the four-day OT Security Professional. The Expert builds on it.
Malware that addresses control systems directly
In 2016 Industroyer used the control system protocols directly, that is IEC 101, IEC 104, IEC 61850 and OPC, without the detour over an operator station. A year later TRITON aimed at the safety system of a plant, at the last protective layer. PIPEDREAM became known in 2022. It is a toolkit for a whole class of devices, not a tool for one target. Switch the operating mode, read and write programs, communicate over OPC UA and Modbus, all of it prepared.
Malware like this is not recognised by its file name. It shows up when someone reads the protocol it speaks, can name its capabilities in the code and writes a rule that catches its traffic. A test environment helps little here. Without the target device it wants to address, the malware does not show its behaviour.
That is hands-on work. It is the subject of this training.
Teaching format and lab environment
The Professional lays the foundation with how a plant is built, its protocols, the plant architecture and attack detection. The Expert builds the skills on top, in three days. Around 80 per cent of the course is hands-on exercises.
The three days build on each other. Whoever has read a protocol themselves can attack with it. Whoever has attacked themselves knows what is in their own capture. They notice straight away what their detection rule misses. That is why on the third day every team writes rules on the recordings it produced itself on the second.
Two people work at each plant with real industrial controllers. In addition every person has a virtual plant of their own, on which steps can be repeated without waiting for the device.
This is supplemented by curated captures from field devices, on which methods can be reproduced that do not occur on the course plant.
That is the difference to the Professional. It practises in a virtual waterworks and therefore also runs remotely. The Expert is on site, because the devices have to be in the room.
Day 1: Protocols
Every team works against its own instance of the course plant. It delivers the same process values over several protocols at once. There is a reason for that. Where a register carries no name, a second protocol reveals which quantity is behind it. So nothing is guessed. With every protocol we follow the same four steps. First read with the standard tool, then build a request of your own, then work through the undocumented address space, finally take a telegram apart by hand.
- Zones and test planning. Derive from a plant's zone concept a test plan that records what may be tested and who approves it
- Modbus TCP and RTU. Analyse the traffic, build your own requests and use them to read and write registers deliberately
- S7comm and S7comm-plus. Tell the two Siemens protocols apart. The classic one transmits unprotected, the newer one secures integrity
- Profinet DCP. Track down devices at Ethernet level, before an IP address is involved at all
- OPC UA. Search the address space and assess which security policy a server really offers and whether anonymous login is open
- BACnet/IP. Building automation on the same network, where a single broadcast lists every device on a site
- An unknown protocol. Derive the structure from the capture alone, without a specification and without a ready-made dissector
- Real captures. Check your own results against recordings from real field devices
Day 2: Offensive OT security
First known attacks on control systems are taken apart, then the same techniques are run under control against the course plant. Every team records while doing so. These recordings are the material for day 3.
- Case analysis. We take Industroyer, Industroyer2, TRITON and PIPEDREAM apart. For each case we record which protocol was attacked, which capability the malware brought along and where it stood in the ICS Kill Chain
- MITRE ATT&CK for ICS. Every step of your own in the lab is mapped to a technique, not only the steps from the case studies
- Reconnaissance and its traces. We measure how much traffic each method produces and how much of it becomes visible in the control room
- Process manipulation. Change setpoints and registers. Force an output so that the control program no longer overwrites it. Each of these interventions stands out to a different degree
- Attacks on the controller. Switch the operating mode, read and write programs, assess the protection levels at Siemens and Codesys
- Identity manipulation. Change device identifiers over Profinet DCP and see why that is harder to clear up forensically
- The route from IT into OT. Reconstruct a real attack path and determine the most effective countermeasure
- Classes of intervention. Before every command, record what it triggers, who approves it and how to undo it
Day 3: Defensive OT security
Analyse malware and build detection, on the recordings from the previous day. No endpoint agent runs on a controller, so the familiar source falls away. That is why we build three others, one after another. Detection through signatures, detection through deviation from a baseline, and checking device and process integrity.
- ICS malware triage. Classify an unknown malicious program without a target device and without a usable test environment. Its capabilities can be read off the protocol code
- YARA. Derive a rule from the malicious program and then check whether it also fires on harmless files
- Intrusion detection for OT. Turn industrial protocols such as Modbus, S7comm, IEC 104 and Profinet into events that can be evaluated
- Rules and signatures. Write your own detection rules for these protocols and check rule sets from others for fitness
- Baselining and whitelisting. Define which devices may communicate with each other and which function codes are allowed. Everything else stands out, even without a signature
- Process aware detection. Check setpoints and measured values for physical plausibility instead of only looking at packets
- Device integrity. Compare program versions and checksums of a controller where no agent is available
- SIEM and use cases. Connect messages from OT sources, formulate use cases following MITRE ATT&CK for ICS and keep the alert flood in check
- Detection engineering. Every rule is tested against your own capture from the previous day before it counts as finished
- Final exercise and report. You work an incident where the material is incomplete. For it you write a technical report with the reporting duties under NIS2
Final exercise and certificate
The third day ends with a final exercise. For it every team writes an incident report of its own, with the finding, the level of evidence and what remained unchecked.
Afterwards you receive a certificate of attendance from Yekta IT. It states the scope of 24 teaching units, the contents and the final exercise. It can be used as evidence of training under NIS2. Whether it suffices in a given case is for your supervisory authority to decide.
Formats
Both routes are held in German and on site. Remote is not possible for the Expert, the devices have to be in the room.
In-house training
For a team from your own company, at your site or in our lab. We arrange the date by agreement.
Open date
For individual participants, eight people at most. We arrange dates on request. Tell us your preferred period in the form.
Trainer
Frequently asked questions
That depends on the format, on the number of participants and on whether we come to you. Leave your details below and you get the terms and a named contact.
We arrange dates on request, for in-house and for open courses alike. Tell us your preferred period in the form and we come back with concrete dates.
Not necessarily, but comparable practical experience is required. If you are unsure, talk to us, we can place it in five minutes.
Yes. Two people work at each plant with real industrial controllers. In addition every person has a virtual plant of their own for the steps that can be repeated.
A notebook with administrator rights, Docker able to run, Wireshark installed. Lab access, materials and all captures and scripts are provided by us.
The certificate states scope, contents and the final exercise and can be used as evidence of regular training. Whether it suffices in a given case is for your supervisory authority to decide.
Not without further ado. What is allowed in the course on the course plant needs an approval, a time window and a way back at your plant. That is exactly the subject of an OT penetration test.
Ask about dates and terms
Tell us the format and the number of participants. You get dates, terms and a named contact.